
PHP Vulnerability Assessment: CVE-2026-109618 and CVE-2026-109619
UROVO devices running UROVO-supplied standard firmware are not affected by these two PHP vulnerabilities, and no device firmware update is required.
 i9200
New
 i9200(Non-financial)
New
 i5300L
New
 i5300
New
 i9100
 i9000S
 i5000
 Q200
 SP35
New
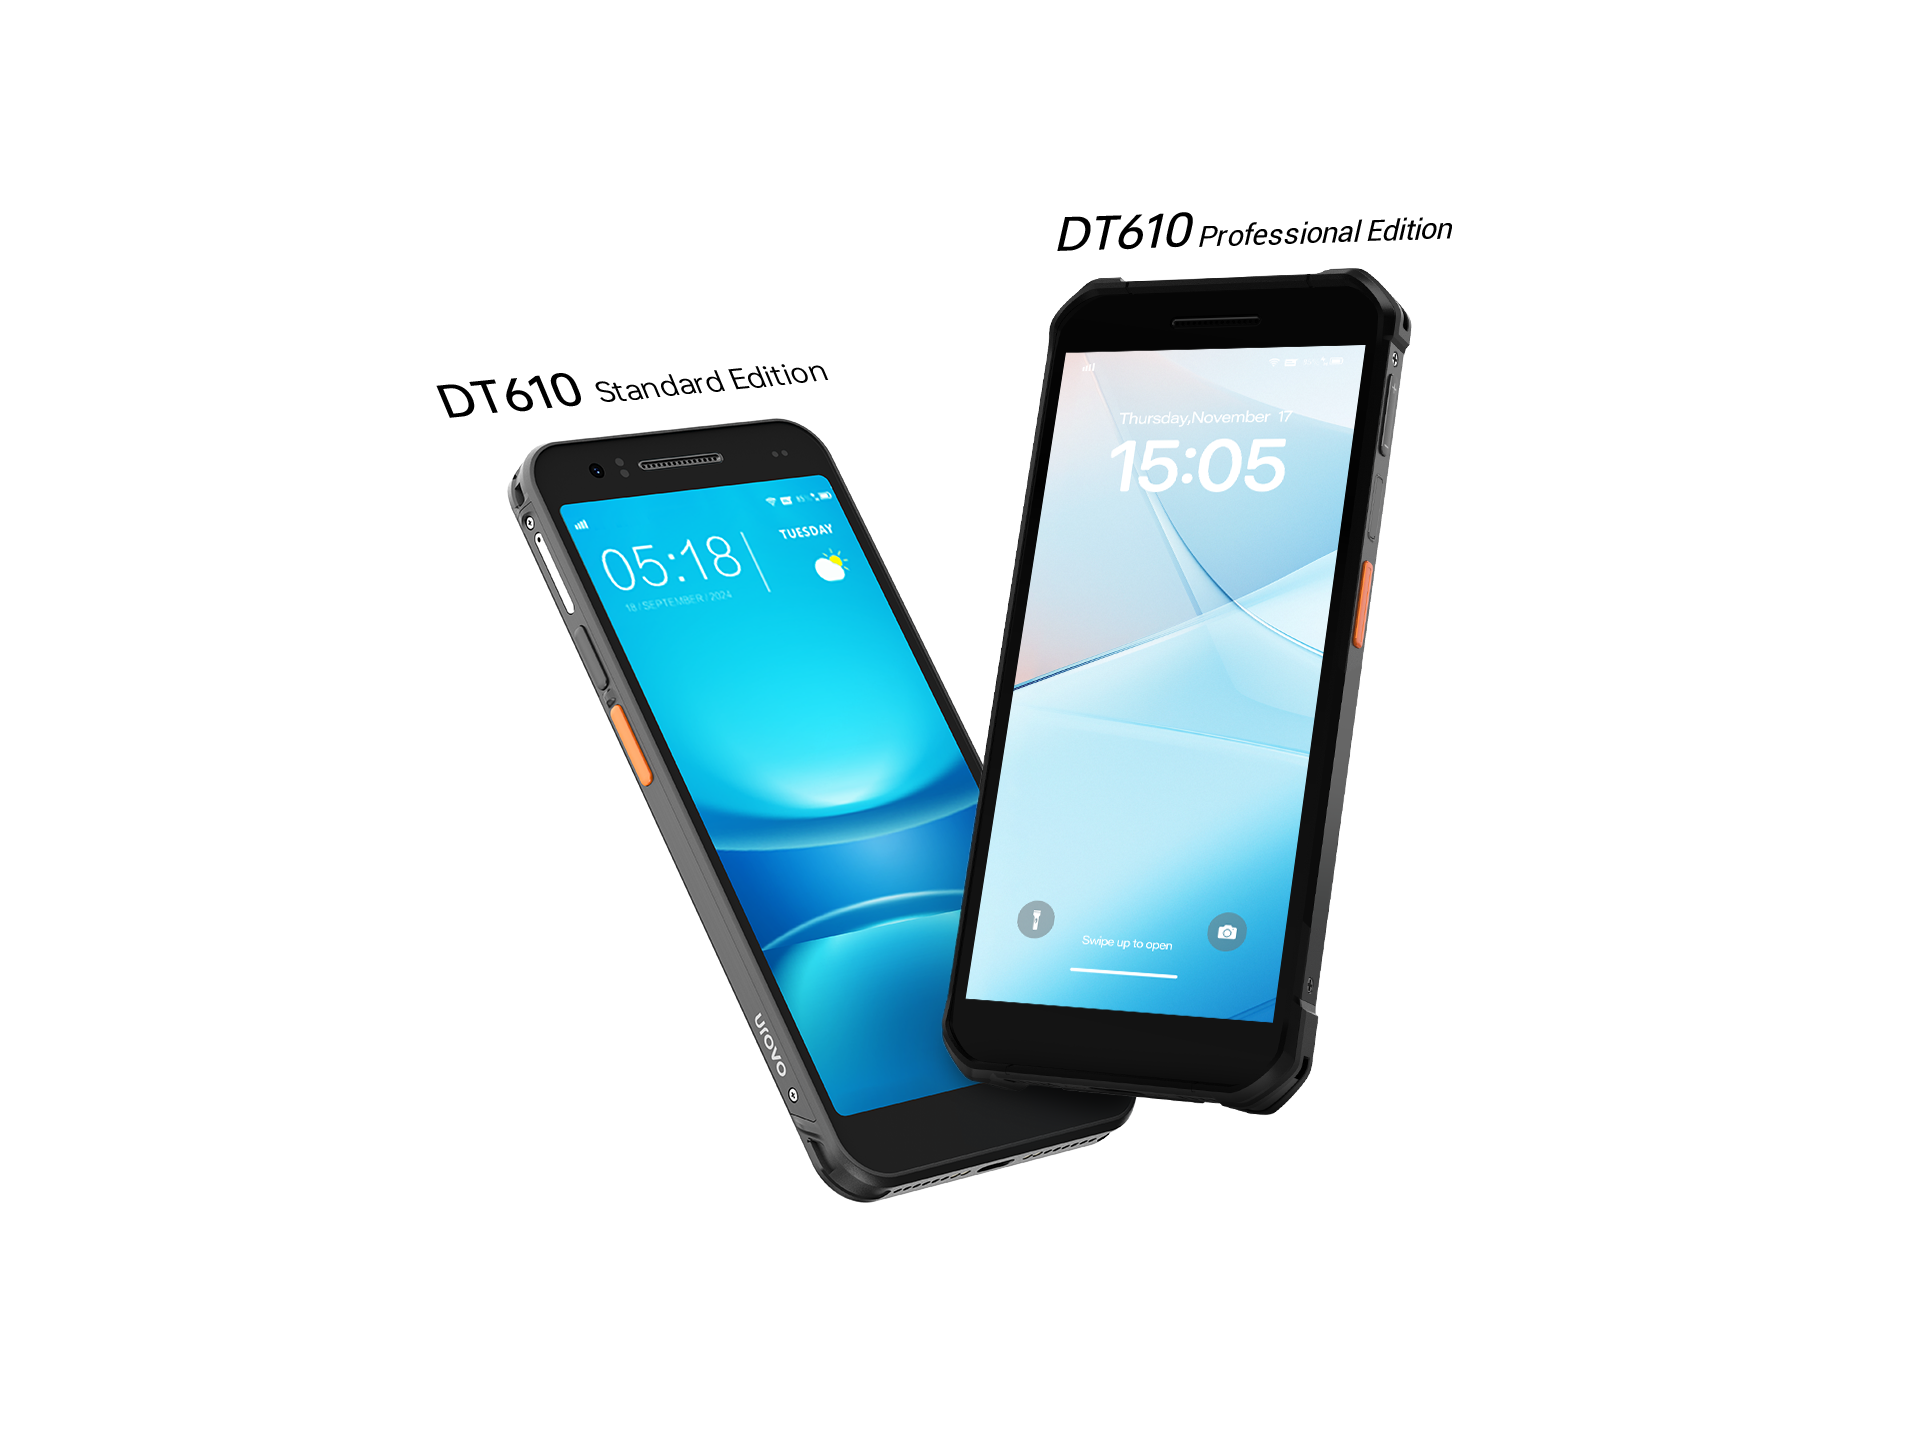 DT610
New
 DT66
New
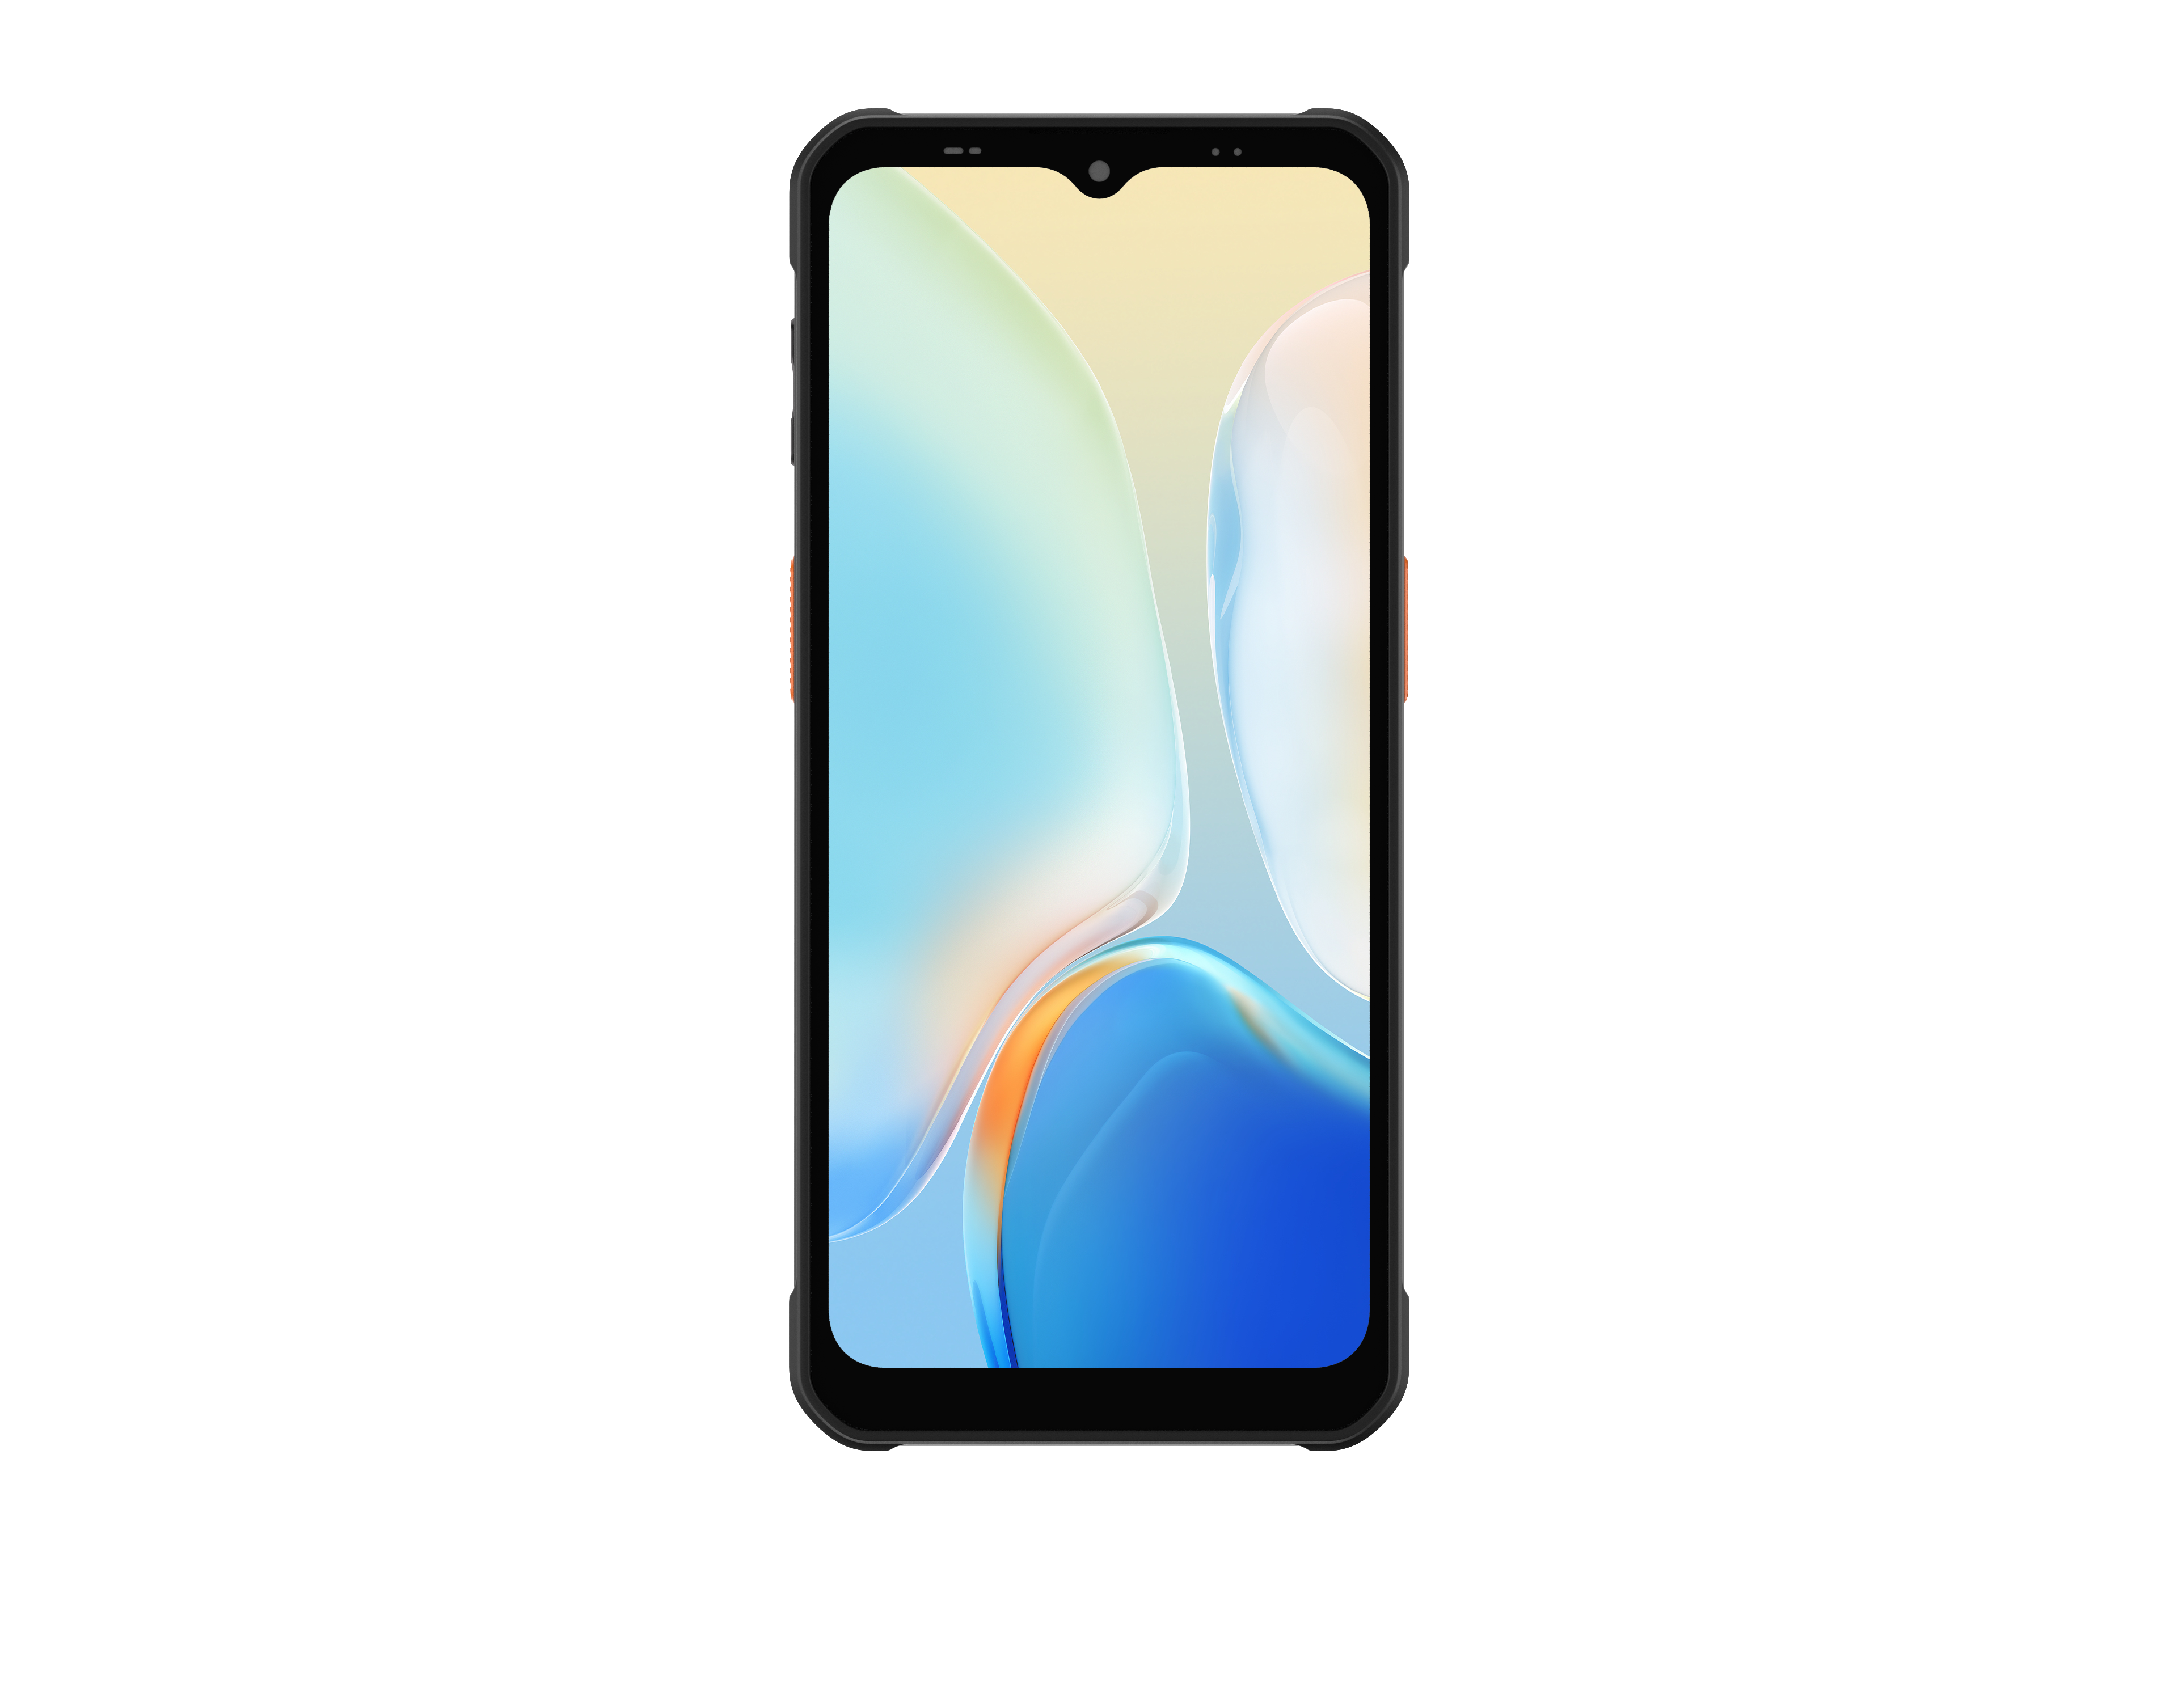 DT630
New
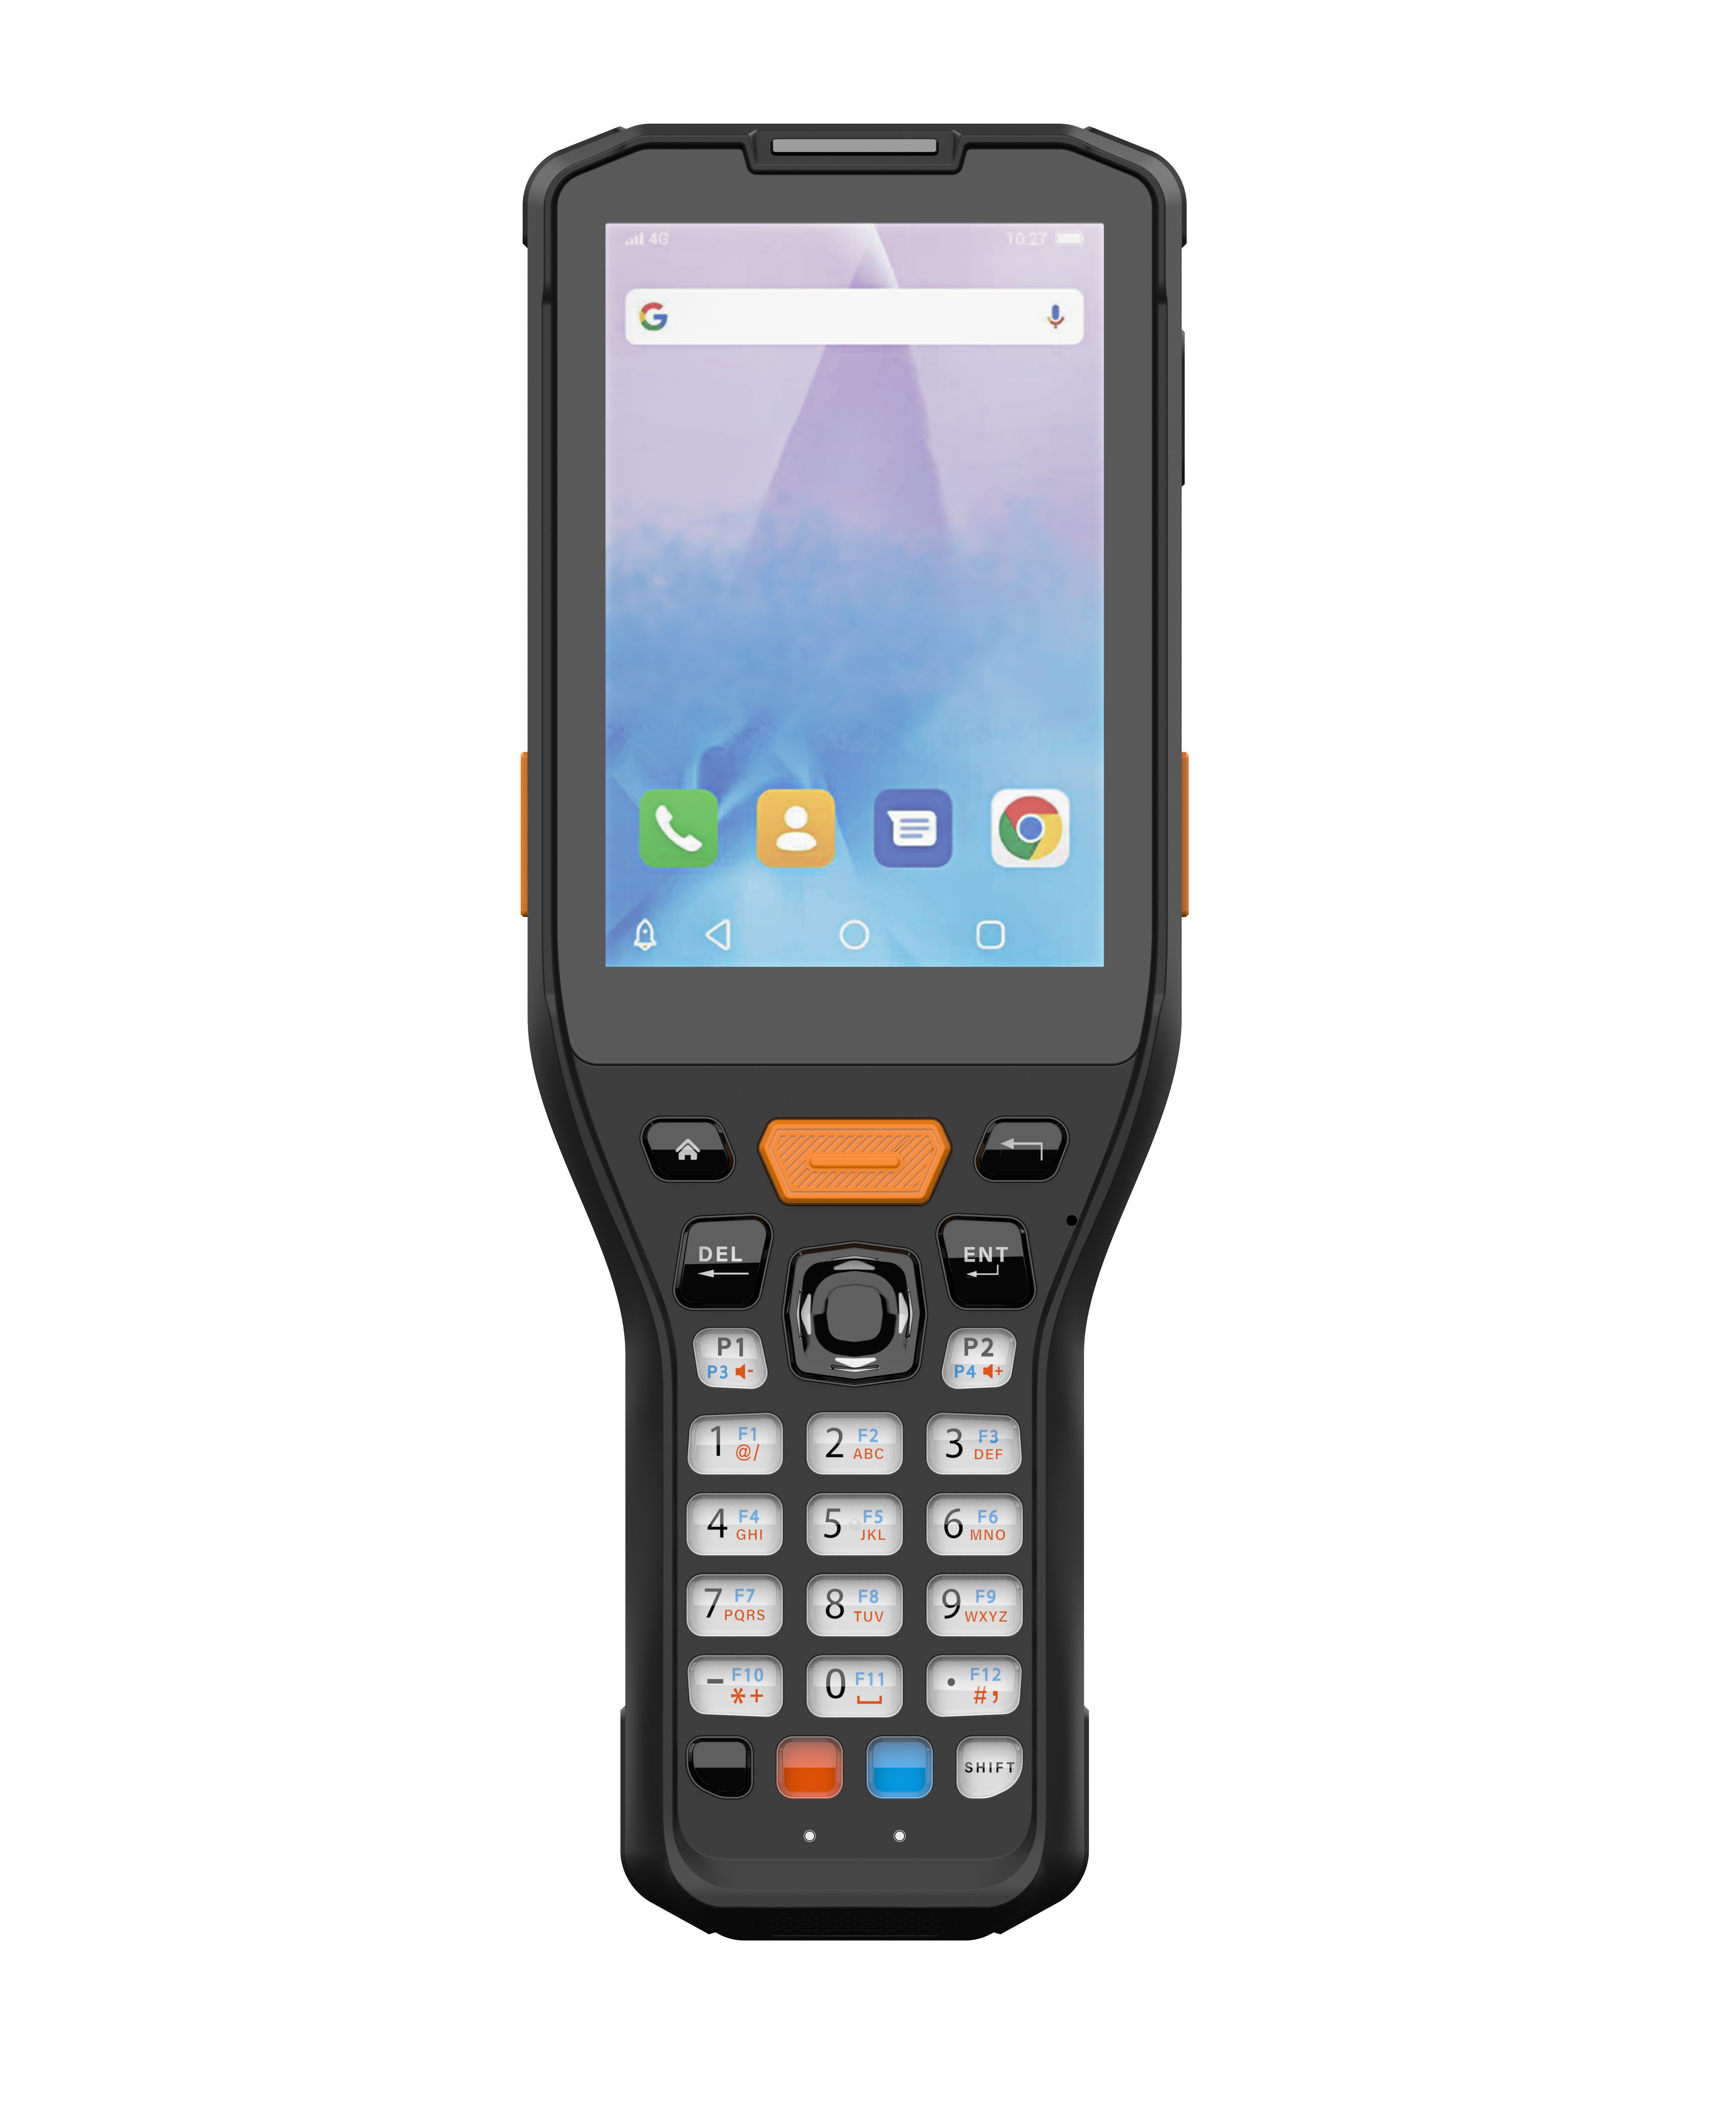 RT30
New
 DT50
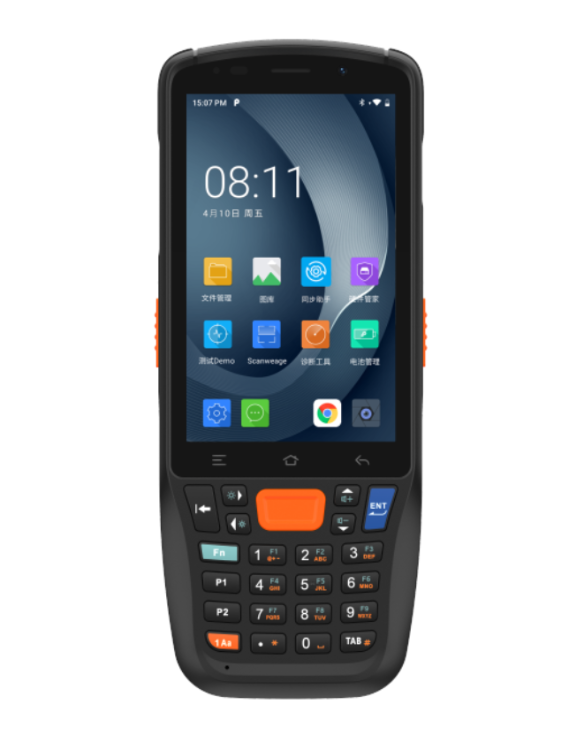 CT48C
 CT58C
 DT50 5G
 DT40
 RT40S
 U2S
New
 R7 Series
 DT50P Lite
New
 DT50(P)
 DT50(D)
 FR7000 Series
New
 FR2000
New
 FR1000
 RFG91
New
 K388 Pro
New
 D81R Series
New
 UROVO Healthcare Devices
Tablets
 U100
New
 P8100 4G
 P8100P Series
 K180
New
 K200
New
 K220
Printers
 K329
 K419


UROVO’s Product Security Incident Response Team (PSIRT) receives, validates, coordinates, remediates and discloses security vulnerabilities affecting UROVO products.
UROVO manages vulnerability remediation through a risk-based process and coordinates with relevant platform, chipset and component providers when required.
Submit a potential vulnerability through UROVO’s official support or security channel.
Receipt is normally acknowledged within 1 business day.
An initial assessment is normally completed within 5 business days.
Confirmed issues are handled according to severity, product impact and available fixes or mitigations.
Where appropriate, UROVO publishes relevant security information, fixes or mitigation guidance.
For device-specific Android security patch information, continue using UROVO’s current security patch page.
The following entries summarize security vulnerabilities selected for public disclosure. Select a CVE ID or source link to view the corresponding official security bulletin.
UROVO devices running UROVO-supplied standard firmware are not affected by these two PHP vulnerabilities, and no device firmware update is required.
If you believe you have identified a potential security vulnerability affecting a UROVO product, please contact UROVO through the official security email and include the affected product/model, software or firmware version, issue description, reproduction steps and relevant evidence where available.
UROVO’s Product Security Incident Response Team (PSIRT) receives, validates, coordinates, remediates and discloses security vulnerabilities affecting UROVO products.
UROVO manages vulnerability remediation through a risk-based process and coordinates with relevant platform, chipset and component providers when required.
Submit a potential vulnerability through UROVO’s official support or security channel.
Receipt is normally acknowledged within 1 business day.
An initial assessment is normally completed within 5 business days.
Confirmed issues are handled according to severity, product impact and available fixes or mitigations.
Where appropriate, UROVO publishes relevant security information, fixes or mitigation guidance.
For device-specific Android security patch information, continue using UROVO’s current security patch page.
The following entries summarize security vulnerabilities selected for public disclosure. Select a CVE ID or source link to view the corresponding official security bulletin.
UROVO devices running UROVO-supplied standard firmware are not affected by these two PHP vulnerabilities, and no device firmware update is required.
If you believe you have identified a potential security vulnerability affecting a UROVO product, please contact UROVO through the official security email and include the affected product/model, software or firmware version, issue description, reproduction steps and relevant evidence where available.